Broadcast domains
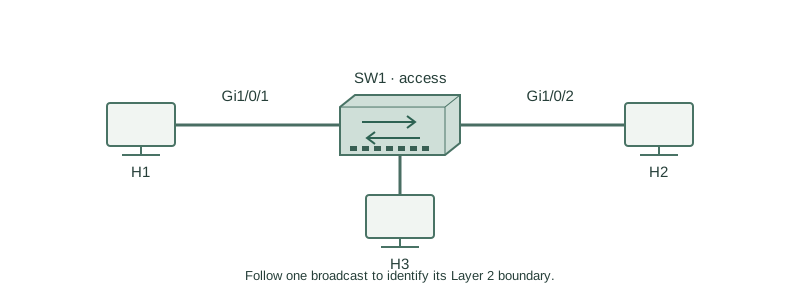
Follow one broadcast to identify its Layer 2 boundary.
Independent lab examples; selected output and frame summaries are illustrative. Port naming and command support vary by switch and software release.
Network and objective
Normal VLAN forwarding is assumed, with no isolation or storm suppression.
Three access hosts use VLAN 10 on SW1. A routed interface provides access to a different subnet.
How it works
An Ethernet broadcast has destination ff:ff:ff:ff:ff:ff. It is replicated to eligible forwarding ports in the ingress VLAN except the receiving port. ARP requests are a familiar example; unknown unicast may use the same egress set but retains its original unicast destination.
A VLAN defines a Layer 2 broadcast domain across the trunks carrying it. Ordinary routing does not forward the received Ethernet broadcast frame into a second VLAN. A configured application relay, such as DHCP relay, can create a separate routed message; this does not merge the broadcast domains.
Configure or inspect
vlan 10
interface range GigabitEthernet1/0/1 - 3
 switchport mode access
 switchport access vlan 10
Verify the result
SW1#show vlan brief
VLAN Name                             Status    Ports
10   VLAN0010                         active    Gi1/0/1, Gi1/0/2, Gi1/0/3
Reconstructed frame on Gi1/0/1:
  Destination ff:ff:ff:ff:ff:ff, EtherType 0x0806 (ARP)
An ARP request received from H1 is eligible for Gi1/0/2 and Gi1/0/3, not a port in another VLAN. The frame summary is illustrative, not a capture.
Failure and recovery
If an expected listener misses the broadcast, inspect VLAN membership, trunk carriage, spanning-tree state and policy. Do not conclude that clearing the sender’s ARP cache changes the Layer 2 boundary.
Restore the intended VLAN membership or trunk path, then test with one known broadcast and a matching observation point.
Further reading
Key Takeaways
- Broadcast is identified by its destination MAC.
- A VLAN bounds ordinary Layer 2 broadcast flooding.
- Trunks can extend that VLAN across switches.
- Routing separates broadcast domains.
- Unknown unicast flooding is not address rewriting.