Dynamic ARP Inspection
Validate ARP on untrusted ports using the expected IP-to-MAC bindings.
Independent lab examples; selected output and frame summaries are illustrative. Port naming and command support vary by switch and software release.
Network and objective
IPv4 DAI on supported switches. DHCP snooping, DAI trust, and inspection rate limits are distinct settings.
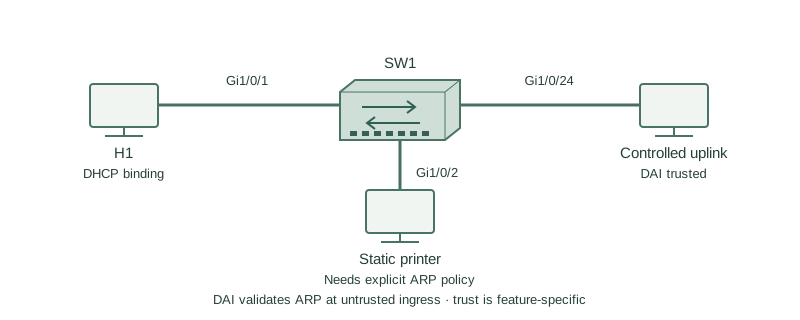
H1 has DHCP binding 192.168.10.10 / 0200.0000.0010 on Gi1/0/1, VLAN 10. The controlled upstream network is Gi1/0/24. Enable DAI only after valid bindings and gateway behavior are understood.
How it works
DAI inspects ARP requests and replies entering untrusted interfaces. A sender claiming an IP/MAC pair inconsistent with the trusted database is dropped; ordinary IP packets are not validated by this ARP-specific feature.
DHCP snooping supplies bindings for leased clients. Static-addressed endpoints need a supported ARP ACL or equivalent documented design. DHCP snooping trust does not automatically mean DAI trust; configure and audit them separately.
A trusted DAI interface bypasses inspection, so it must lead to a controlled network that enforces the policy appropriately. Rate limits can protect processing resources but can also error-disable a port during legitimate bursts; choose limits based on observed traffic and platform behavior.
Configure or inspect
ip dhcp snooping
ip dhcp snooping vlan 10
ip arp inspection vlan 10
interface GigabitEthernet1/0/24
 ip dhcp snooping trust
 ip arp inspection trust
Verify the result
SW1#show ip arp inspection statistics vlan 10
Vlan  Forwarded  Dropped  DHCP Drops  ACL Drops
10    42         3        3           0
SW1#show ip dhcp snooping binding
02:00:00:00:00:10 192.168.10.10 3500 dhcp-snooping 10 Gi1/0/1
Three rejected ARP claims did not match the permitted binding policy. Counters alone do not identify intent; correlate inspection logs, ingress interface, sender fields, and the DHCP binding before declaring an attack.
Failure and recovery
A legitimate static printer has no DHCP binding, so enabling DAI causes its ARP replies to fail.
arp access-list STATIC-HOSTS
 permit ip host 192.168.10.50 mac host 0200.0000.0050
exit
ip arp inspection filter STATIC-HOSTS vlan 10
Further reading
Key Takeaways
- DAI checks ARP, not every IP packet.
- DHCP bindings must be valid.
- Static hosts need explicit policy.
- DAI and DHCP trust are separate.
- Inspect counters and rate-limit behavior.