EVPN ARP Suppression
Compare a missing binding with a valid remote binding, then observe when an ARP request can be answered locally.
Use one L2 VNI and a learned IP/MAC binding
This independent lab retains one spine reflector/RP and two VTEPs. H1 and H2 use 10.10.10.11/24 and .22/24 in VNI 10010. Both leaves host Vlan10 with the common gateway address 10.10.10.254 and MAC 0000.2222.3333. The SVI/gateway satisfies this platform model’s requirements; cross-subnet routing is not the test here.
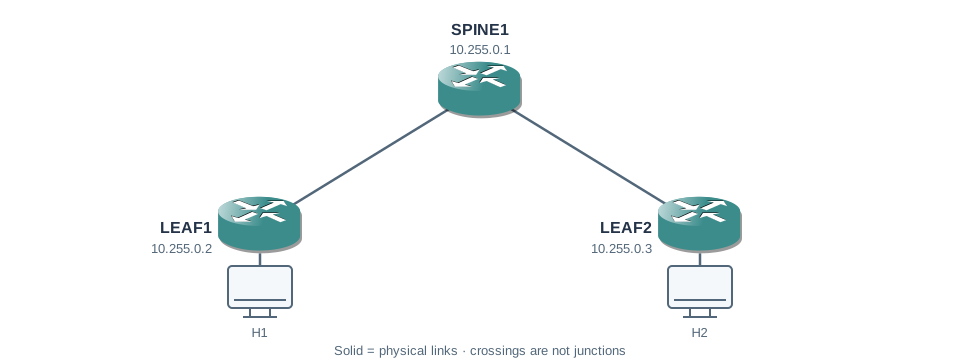
| Physical link | Address at first endpoint | Address at second endpoint |
|---|---|---|
| SPINE1 Ethernet1/1 ↔ LEAF1 Ethernet1/1 | 192.0.2.1/30 | 192.0.2.2/30 |
| SPINE1 Ethernet1/2 ↔ LEAF2 Ethernet1/1 | 192.0.2.5/30 | 192.0.2.6/30 |
| Device | Loopback0 / router ID |
|---|---|
| SPINE1 | 10.255.0.1/32 |
| LEAF1 | 10.255.0.2/32 |
| LEAF2 | 10.255.0.3/32 |
Learn local and remote bindings
| Binding source | Evidence |
|---|---|
| Local endpoint ARP or discovery | The VTEP associates an IP with a local MAC and attachment. |
| Remote EVPN advertisement | A Type 2 MAC/IP route carries the binding to other VTEPs. |
| MAC-only reachability | A remote MAC can be known without an IP binding for suppression. |
A silent endpoint may not have supplied an IP binding yet. BGP establishment alone cannot populate every endpoint. Proxying from stale or duplicate bindings can misdirect traffic, so binding validity and withdrawal behavior matter.
Enable suppression for this VNI
Both leaves · prerequisites and suppression
feature interface-vlan
fabric forwarding anycast-gateway-mac 0000.2222.3333
interface Vlan10
  no shutdown
  ip address 10.10.10.254/24
  fabric forwarding mode anycast-gateway
interface nve1
  member vni 10010
    suppress-arp
Apply these settings to the complete EVPN/VLAN/PIM baseline below, not to the earlier data-plane-only lab. Some ASIC families require ARP TCAM allocation and a reload; validate the specific platform before enabling this feature. It is not a universal single-command guarantee for every image.
Cache miss: retain the discovery path
Access: who has 10.10.10.22? tell 10.10.10.11
LEAF1 suppression lookup: no valid binding
Expected next action: flood according to VNI BUM policy
H2 reply permits local and remote binding learning
A miss cannot safely be answered with an invented MAC. This lab’s multicast group remains the fallback discovery path. If unknown-unicast or ARP flooding is separately disabled, a silent-host failure is a policy consequence, not proof that suppression should know the host already.
Cache hit: proxy the remote endpoint
LEAF1# show ip arp suppression-cache
IP address       MAC address       VNI    Source
10.10.10.22 0200.0000.0022 10010 remoteAccess request: who has 10.10.10.22?
LEAF1 replies on behalf of H2: 10.10.10.22 is 02:00:00:00:00:22
This request need not traverse the VXLAN multicast tree
Subsequent H1-to-H2 data still crosses the fabricThe reply supplies H2’s MAC, not the anycast gateway MAC for a same-subnet H2 query. Contrast a transport capture before and after the binding appears. Suppression reduces this ARP flooding; it does not eliminate all broadcast, multicast or unknown traffic.
Validate stale, missing and disabled states
First verify the Type 2 IP/MAC route and local suppression cache for the same VNI. A known remote MAC with no IP binding can still forward data but cannot answer an arbitrary IP query. For a deliberate missing-binding test, use an isolated clean endpoint exchange rather than erase unrelated production state. To compare behavior without suppression, remove suppress-arp from the VNI on both leaves, repeat the test, then restore it and verify a refreshed valid binding.
Complete independent lab configurations
Start with clean isolated lab devices. These are the complete scenario configurations, not changes to apply on top of a different lesson. Physical ports must match the address table. Virtual-image data-plane capabilities can differ from physical switches; these examples have not been executed on live devices.
Download configuration reference
SPINE1
hostname SPINE1
feature ospf
feature pim
ip pim rp-address 10.255.0.1 group-list 239.1.1.0/24
router ospf UNDERLAY
  router-id 10.255.0.1
interface loopback0
  ip address 10.255.0.1/32
  ip router ospf UNDERLAY area 0.0.0.0
  ip pim sparse-mode
interface Ethernet1/1
  no switchport
  mtu 9216
  ip address 192.0.2.1/30
  ip ospf network point-to-point
  ip ospf cost 40
  ip router ospf UNDERLAY area 0.0.0.0
  ip pim sparse-mode
  no shutdown
interface Ethernet1/2
  no switchport
  mtu 9216
  ip address 192.0.2.5/30
  ip ospf network point-to-point
  ip ospf cost 40
  ip router ospf UNDERLAY area 0.0.0.0
  ip pim sparse-mode
  no shutdown
feature bgp
nv overlay evpn
router bgp 65000
  router-id 10.255.0.1
  address-family l2vpn evpn
  neighbor 10.255.0.2
    remote-as 65000
    update-source loopback0
    address-family l2vpn evpn
      send-community
      send-community extended
      route-reflector-client
  neighbor 10.255.0.3
    remote-as 65000
    update-source loopback0
    address-family l2vpn evpn
      send-community
      send-community extended
      route-reflector-client
LEAF1
hostname LEAF1
feature ospf
feature pim
ip pim rp-address 10.255.0.1 group-list 239.1.1.0/24
router ospf UNDERLAY
  router-id 10.255.0.2
interface loopback0
  ip address 10.255.0.2/32
  ip router ospf UNDERLAY area 0.0.0.0
  ip pim sparse-mode
interface Ethernet1/1
  no switchport
  mtu 9216
  ip address 192.0.2.2/30
  ip ospf network point-to-point
  ip ospf cost 40
  ip router ospf UNDERLAY area 0.0.0.0
  ip pim sparse-mode
  no shutdown
feature nv overlay
feature vn-segment-vlan-based
vlan 10
  vn-segment 10010
interface Ethernet1/2
  switchport
  switchport mode access
  switchport access vlan 10
  spanning-tree port type edge
  no shutdown
interface nve1
  no shutdown
  source-interface loopback0
  host-reachability protocol bgp
  member vni 10010
    mcast-group 239.1.1.1
evpn
  vni 10010 l2
    rd auto
    route-target import 65000:10010
    route-target export 65000:10010
feature bgp
nv overlay evpn
router bgp 65000
  router-id 10.255.0.2
  address-family l2vpn evpn
  neighbor 10.255.0.1
    remote-as 65000
    update-source loopback0
    address-family l2vpn evpn
      send-community
      send-community extended
feature interface-vlan
fabric forwarding anycast-gateway-mac 0000.2222.3333
interface Vlan10
  no shutdown
  ip address 10.10.10.254/24
  fabric forwarding mode anycast-gateway
interface nve1
  member vni 10010
    suppress-arp
LEAF2
hostname LEAF2
feature ospf
feature pim
ip pim rp-address 10.255.0.1 group-list 239.1.1.0/24
router ospf UNDERLAY
  router-id 10.255.0.3
interface loopback0
  ip address 10.255.0.3/32
  ip router ospf UNDERLAY area 0.0.0.0
  ip pim sparse-mode
interface Ethernet1/1
  no switchport
  mtu 9216
  ip address 192.0.2.6/30
  ip ospf network point-to-point
  ip ospf cost 40
  ip router ospf UNDERLAY area 0.0.0.0
  ip pim sparse-mode
  no shutdown
feature nv overlay
feature vn-segment-vlan-based
vlan 10
  vn-segment 10010
interface Ethernet1/2
  switchport
  switchport mode access
  switchport access vlan 10
  spanning-tree port type edge
  no shutdown
interface nve1
  no shutdown
  source-interface loopback0
  host-reachability protocol bgp
  member vni 10010
    mcast-group 239.1.1.1
evpn
  vni 10010 l2
    rd auto
    route-target import 65000:10010
    route-target export 65000:10010
feature bgp
nv overlay evpn
router bgp 65000
  router-id 10.255.0.3
  address-family l2vpn evpn
  neighbor 10.255.0.1
    remote-as 65000
    update-source loopback0
    address-family l2vpn evpn
      send-community
      send-community extended
feature interface-vlan
fabric forwarding anycast-gateway-mac 0000.2222.3333
interface Vlan10
  no shutdown
  ip address 10.10.10.254/24
  fabric forwarding mode anycast-gateway
interface nve1
  member vni 10010
suppress-arp| Host | Address | Gateway |
|---|---|---|
| H1 | 10.10.10.11/24 | none |
| H2 | 10.10.10.22/24 | none |
Further reading
Key Takeaways
- ARP suppression needs a valid IP/MAC binding in the intended VNI.
- Local discovery and remote Type 2 IP/MAC routes populate that information.
- A cache miss still needs a working discovery/flooding policy.
- A hit can proxy the remote host MAC locally and reduce ARP flooding.
- Suppression is not authentication and does not eliminate every BUM case.